Cyber insurance requirements for small businesses in 2027 should be reviewed alongside the coverage offered in each quote. Business owners should compare cybersecurity conditions, covered incidents, policy limits, exclusions, and claims support before choosing a policy.
A lower premium may provide limited protection if payment fraud, technology outages, or certain recovery costs are excluded. Employers and HR teams may also handle sensitive employee information, making data protection a business concern. Understanding what insurers ask and how policies differ helps companies make informed coverage decisions before purchasing insurance.
Key Takeaways
- Cyber insurance quotes should be evaluated using covered incidents, policy limits, exclusions, and claims support rather than premium alone.
- Cybersecurity safeguards, including multifactor authentication and secure backups, can influence eligibility and underwriting conditions.
- First-party and third-party cyber coverage address different types of financial losses and liability claims.
- Ransomware, payment fraud, and outside technology incidents may have separate limits or coverage restrictions.
- Comparing policy terms and documenting application answers helps businesses make more informed insurance decisions.
What Should Small Businesses Look for in a Cyber Insurance Quote in 2027?
A small business should look for a cyber insurance quote that matches its technology risks, financial exposure, and ability to respond to an incident. The quote should clearly explain which events qualify for coverage, how much protection is available, and what responsibilities the business must meet. When reviewing cyber insurance requirements for small businesses, focus on these areas:
- Covered incidents: Data breaches, ransomware, network disruptions, and other specified cyber events.
- Security requirements: Safeguards the insurer expects the business to maintain.
- Financial terms: Coverage limits, deductibles, sublimits, and exclusions.
- Business interruption: Protection for qualifying income losses following covered cyber incidents.
- Claims support: Incident reporting procedures, legal assistance, and available recovery services.
Compare proposals using the same business operations and coverage needs. A policy with a lower premium may contain restrictions that make it less suitable for certain exposures.
Businesses should also review existing insurance before adding cyber coverage, since different policies may address different types of losses. For example, a retailer working with an insurance agency in Walterboro, SC may need to compare commercial crime coverage for fraudulent transfers with cyber insurance for data recovery and network interruptions. The same principle applies to businesses nationwide: understanding where one policy ends and another begins helps identify potential coverage gaps.
What Cybersecurity Requirements Should Small Businesses Check Before Applying?
Cyber insurers commonly review security measures before offering coverage. These requirements help insurers evaluate the likelihood of an incident and the possible financial impact on the business. Applications may ask about the company’s technology systems, sensitive information, previous security incidents, and existing protections. Some insurers require particular safeguards, while others evaluate them as part of their underwriting process.
Businesses should understand these conditions before submitting applications. A security measure that has been planned but not implemented should not be reported as active. Accurate information helps insurers assess the business correctly and reduces the risk of later disputes about application answers.
Which Security Controls Do Cyber Insurers Commonly Ask About?
Insurers may ask about multifactor authentication (MFA), which requires users to verify their identity through more than one authentication factor. Other common questions cover endpoint detection and response (EDR), secure backups, software updates, employee phishing training, and restricted administrative access. Requirements differ by insurer, so businesses should confirm which protections are mandatory for their applications.
How Should Businesses Document Their Application Answers?
Businesses should keep records that support their answers about cybersecurity practices. Useful documentation includes MFA settings, backup test results, security training records, software update procedures, and incident response plans. IT staff or outside technology providers can help verify technical information. If a safeguard is incomplete, the application should reflect its actual status rather than planned improvements.
What Coverage Should a Small Business Cyber Insurance Policy Include?
A cyber insurance policy should address the financial losses and liability risks most relevant to the company’s operations. Coverage commonly falls into two categories: first-party losses affecting the insured business and third-party claims involving customers or other parties. Depending on the policy, protection may include breach investigations, data recovery, business interruption, notification expenses, and legal defense.
The Federal Trade Commission’s cyber insurance guidance explains these coverage categories and the services businesses should evaluate. Understanding what business insurance covers can also help employers distinguish cyber protection from general liability, property, and other commercial policies.
First-Party and Third-Party Cyber Coverage
First-party coverage may pay certain expenses the business incurs after a covered incident, including forensic investigations, data restoration, customer notifications, and lost income. Third-party coverage addresses eligible claims brought against the business by affected customers or other parties. For example, a data breach could create recovery expenses for the company and separate legal claims from customers whose information was exposed.
Ransomware, Payment Fraud, and Third-Party Technology Incidents
Cyber policies may address ransomware attacks, fraudulent payment instructions, and incidents involving outside technology providers. Coverage for these events is not automatic. Social engineering fraud, which involves deceiving someone into transferring money or disclosing information, may require separate coverage. Businesses should also understand commercial crime insurance when comparing protection against electronic fraud and financial theft.
What Should Walterboro Businesses Consider When Reviewing Cyber Insurance Quotes?
Walterboro serves as a shopping and dining center for surrounding communities, according to the City of Walterboro. Local retailers, restaurants, and service companies may depend on electronic payments, online reservations, customer records, and cloud-based business systems. When comparing cyber insurance quotes, these businesses should check whether coverage addresses payment fraud, data restoration expenses, and qualifying income losses caused by cyber incidents. A business using outside payment processors or software providers should also review coverage for incidents involving those services.
South Carolina Code Section 39-1-90 establishes breach-notification requirements for businesses handling certain personal identifying information. Notification duties depend on the circumstances, including the type of information involved and whether unauthorized acquisition creates specified risks. The South Carolina Department of Consumer Affairs explains the state’s reporting requirements. Walterboro employers should review whether their cyber quotes include legal assistance, forensic investigations, notification services, and incident response support when a qualifying breach occurs.
How Can Small Businesses Compare Cyber Insurance Quotes Beyond Price?
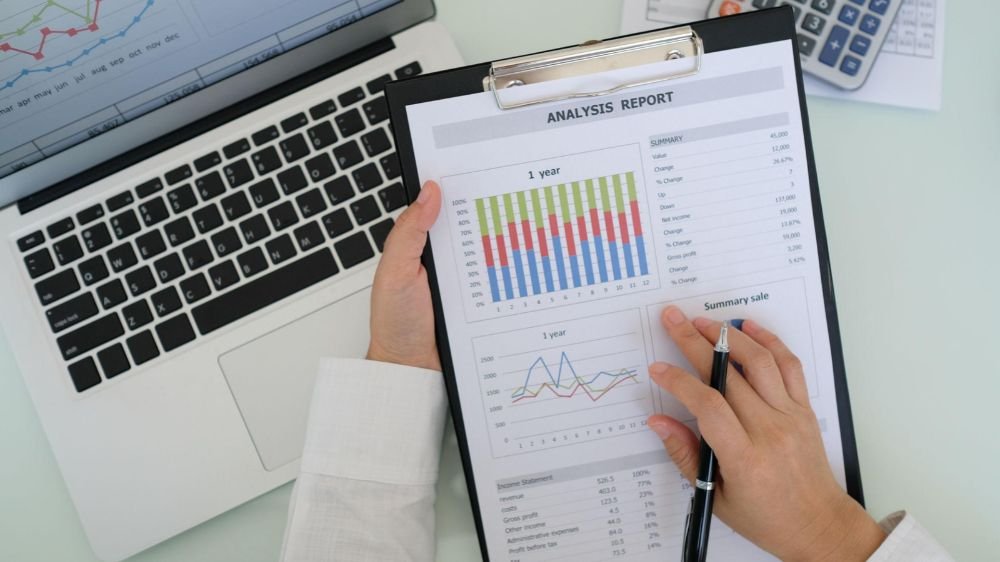
Businesses should compare cyber insurance quotes based on coverage terms and financial protection rather than premium alone. Similar prices do not necessarily provide equivalent coverage. Start by requesting proposals with comparable limits and reviewing the specific cyber incidents each policy addresses. Pay attention to deductibles, separate coverage restrictions, and the support available after an incident. Review existing commercial insurance coverage to determine how cyber protection fits with property, liability, and crime policies. A meaningful comparison should also consider the financial impact of a system outage, the company’s dependence on outside technology, and the expenses it could face while restoring normal operations.
Coverage Limits, Sublimits, Deductibles, and Waiting Periods
A coverage limit is the maximum amount an insurer may pay under specified policy terms. A sublimit places a smaller maximum on a particular category of loss. Deductibles determine the insured business’s share of certain expenses. Waiting periods may delay business interruption coverage. Understanding business interruption insurance also helps distinguish traditional property-related income protection from cyber-related interruption coverage.
Exclusions, Claims Conditions, and Response Services
Exclusions identify events or losses the policy does not cover. Claims conditions explain the steps a business must follow when requesting coverage. Review incident reporting deadlines, security-related conditions, and requirements for using approved response professionals. Some policies provide access to forensic investigators, legal assistance, or breach hotlines. Confirm which services are included and whether their expenses have separate limits.
Which Cyber Insurance Questions Belong on a Quote Checklist?
A cyber insurance checklist helps businesses compare proposals using consistent questions. Before purchasing coverage, ask:
- Which cyber incidents does the policy cover?
- What security measures must we maintain?
- Are first-party and third-party losses covered?
- Does coverage include ransomware and payment fraud?
- What limits, sublimits, and deductibles apply?
- Which exclusions could affect our operations?
- How quickly must we report an incident?
- What claims and recovery services are available?
These cyber insurance questions to ask should be answered using the actual policy wording. Record the answers for each proposal and request clarification about unclear conditions. This creates a practical comparison of coverage rather than relying on premium differences alone.